What gets recorded, and what doesn’t?
Sensitive inputs are masked in the visitor’s browser before anything is sent. Your team’s access is set by role, and you control how much gets recorded.
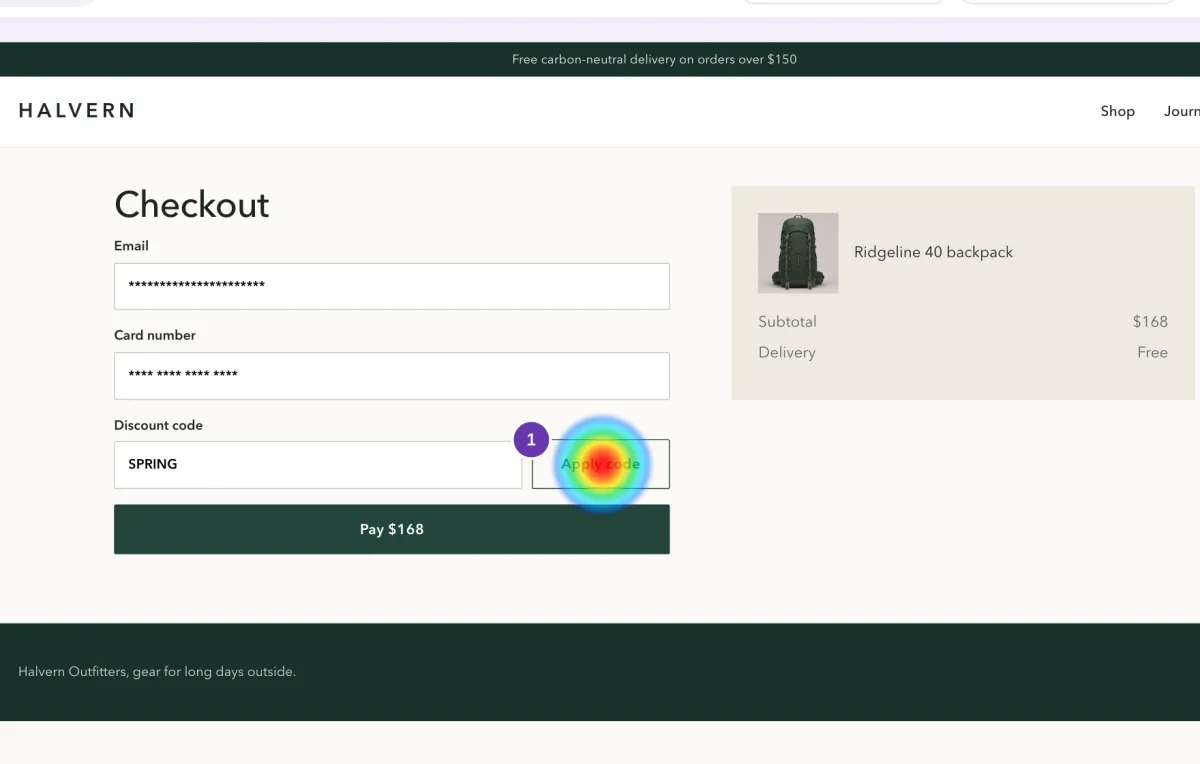
What your visitor types, and what gets recorded
Masking runs in the visitor’s browser, so a masked value never reaches Heatlytics.
Plain text is recorded as typed, unless you mask it.
Always masked. No setting can unmask it.
Always masked, even after a “show password” toggle.
How much gets recorded
Set for each environment, so staging and production can differ.
- Recording
- On
- Sampling
- A share of sessions you set
- Minimum session length
- Skip the shortest visits
- Daily cap per device
- A limit you set
- Allowed domains
- Only the sites you list
- Public key
- Rotate it when you need to
- Masked by default
- Password, hidden, email, phone and number fields, and fields recognised as card or bank details from their name or label, are recorded as asterisks of the same length. Password, hidden and recognised card or bank fields can’t be unmasked by any setting.
- Other fields are your call
- Page text, plain text fields and text areas are recorded as typed unless you mask them, so mark the ones that hold personal details. Long numbers in those fields are masked automatically, whatever the field is called.
- Masking you can set
- Mask or block any element with an attribute or a selector, or mask all text. Images in a masked area become placeholders.
- URLs cleaned too
- Query parameters you list are removed from recorded URLs, including links inside the page.
- Consent built in
- Hold recording until a visitor consents, and use optIn, optOut and abort to follow your consent banner.
- Recording controls
- Per environment: recording on or off, sampling, a minimum session length, a daily cap per device, allowed domains, and a key you can rotate.
Who on your team sees what
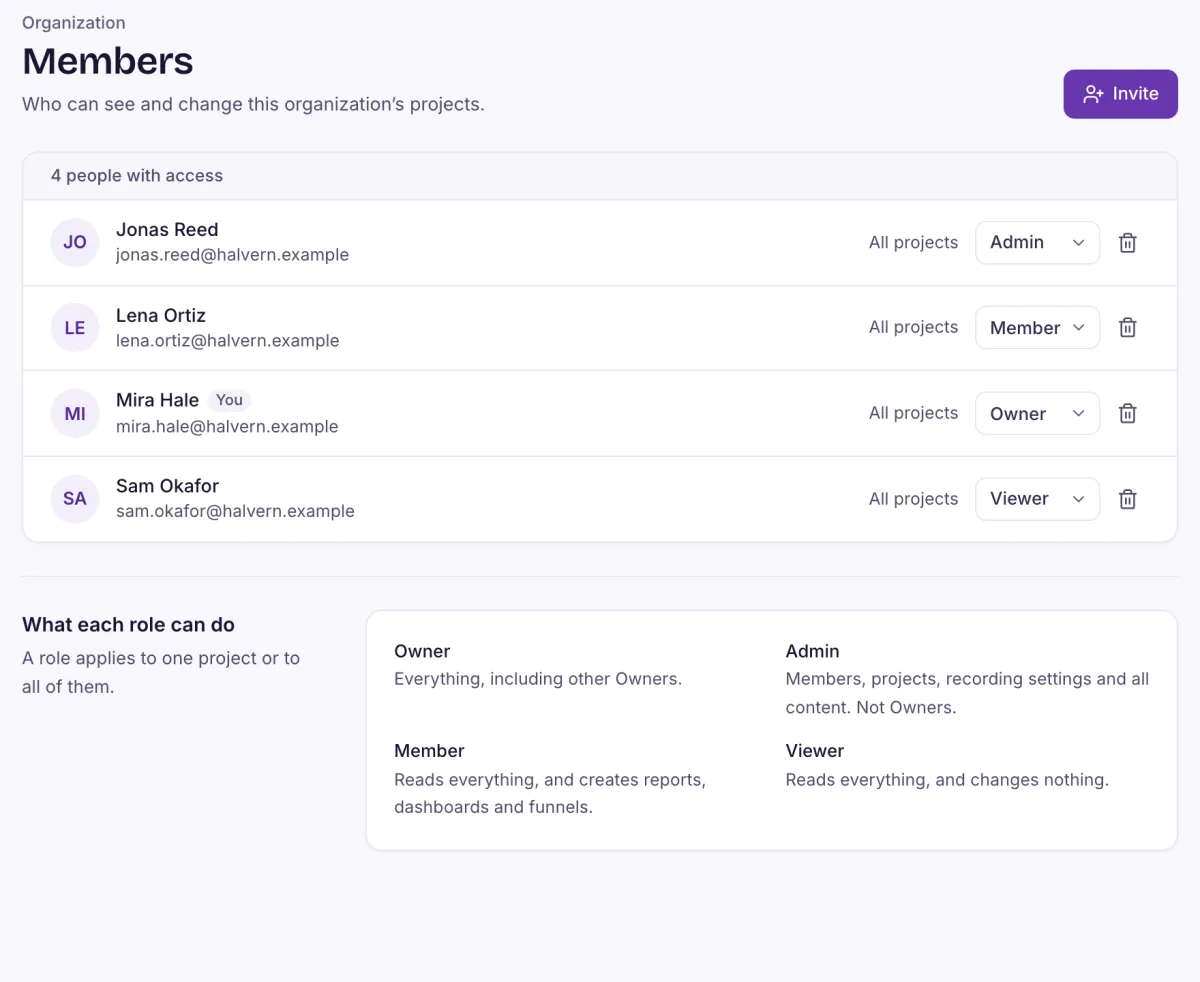
Give each person a role across the organisation or on one project. The same check runs on the server for every page and action.
- Roles
- Owner, Admin, Member and Viewer, across the organisation or per project. Every page and action checks the role on the server.
- Delete a user
- Remove a person and their sessions when they ask. The deletion runs in two passes and keeps a hashed proof.
- IP addresses aren’t stored
- Country and city come from Cloudflare’s location headers, and Heatlytics doesn’t store the address. Data and replay retention are configurable.
What it doesn’t do yet. Retention is set for the whole deployment, not per environment. Single sign-on and two-factor sign-in aren’t available yet.
Bring your privacy questions
We’ll go through what’s recorded on your pages, and what we don’t have yet.